Optimizely Says Attacker Used a Signup Flaw to Inject Malware
/ 6 min read
Summary
The way Optimizely Web works is by having each client load a JavaScript snippet hosted on Optimizely's Content Delivery Network. The practical question is what this changes for SEO, content quality, and AI search visibility.
Websites running Optimizely Web Experimentation served malicious JavaScript to visitors on Nov. 16 after an attacker added it to their projects inside Optimizely.
The code swapped crypto wallet addresses, looked for payment cards typed into sites' own forms, and loaded exploit kits aimed at iPhones and iPads running older versions of iOS. Scott Helme, founder of Report URI, a company that sells tools for monitoring the scripts that run on websites, reported finding the code in snippets belonging to 178 organizations, including Zoom, the BBC, CNN, Salesforce and GitLab.
How The Code Reached Customer Sites
The way Optimizely Web works is by having each client load a JavaScript snippet hosted on Optimizely's Content Delivery Network (CDN). In addition to the client specific experiment data, this snippet can have an optional Project JavaScript. The measurement question is whether this signal changes a decision, not whether it adds another number to a dashboard. Useful reporting connects visibility, engagement, and business outcomes without pretending every AI influenced journey will produce a clean click path.
The reporting question is whether this signal changes a decision. If it only creates another number in a dashboard, it adds noise. If it helps separate profile activity, website visits, calls, bookings, and direction requests, it can make local performance easier to understand.
What The Injected Code Did
Helme found that the inserted code would load a second script which would replace cryptocurrency wallet addresses with the attacker's. Starting at 1:43 p.m. UTC, it would watch the website's own form fields for credit card information,. The measurement question is whether this signal changes a decision, not whether it adds another number to a dashboard. Useful reporting connects visibility, engagement, and business outcomes without pretending every AI influenced journey will produce a clean click path.
Why Content Security Policies Mostly Didn't Stop It
The Content Security Policy (CSP), as a header, tells the browser the scripts that a website can use (the script src section) and to which locations it may transmit data (the connect src section). Report URI then compared those policies. Local visibility depends on whether the details across pages, profiles, categories, reviews, photos, and service descriptions reinforce the same answer for a specific location based query.
What To Check In Optimizely
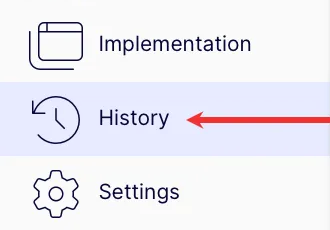
Helme says the Project JavaScript in all of the Optimizely Web customer projects and the custom JavaScript in their experiments should be opened to find 1688360.cc, atob( and any other scripts that were written by someone other than the. The practical question is what this changes in the system: the page structure, the evidence presented, the measurement habit, or the way the topic is connected to related work.
The risk is usually hidden in the execution layer. A page can look fine to a human and still fail for an automated visitor if the form, call to action, rendering path, or confirmation step is not accessible enough for the agent to complete the task.
Why This Matters
Project JavaScript is run on every page that loads an Optimizely snippet, so this attack was able to hit visitors without changing anything on the affected sites' own code. The change sat in customers' Optimizely projects, which put your. The measurement question is whether this signal changes a decision, not whether it adds another number to a dashboard. Useful reporting connects visibility, engagement, and business outcomes without pretending every AI influenced journey will produce a clean click path.
Looking Ahead
Optimizely told BleepingComputer it's continuing to investigate and will publish updates on its status page, which listed the incident as Monitoring on the morning of Nov. 17. Its status page, X post and statement don't say how many. The practical question is what this changes in the system: the page structure, the evidence presented, the measurement habit, or the way the topic is connected to related work.
The practical value is in connecting the idea to an observable signal. That means deciding what should be checked, what would prove the issue is real, and where the team should make the smallest useful improvement first.
How The Code Reached Customer Sites in practice
Introduction Websites running Optimizely Web Experimentation served malicious JavaScript to visitors on Nov. 16 after an attacker added it to their projects inside Optimizely. The code swapped crypto wallet addresses, looked for payment. Local visibility depends on whether the details across pages, profiles, categories, reviews, photos, and service descriptions reinforce the same answer for a specific location based query.
What the visibility signal actually changes
What the visibility signal actually changes: optimizely Says Attacker Used a Signup Flaw to Inject Malware: the Practical Angle should be treated as a visibility signal, not a standalone headline. Introduction Websites running Optimizely Web Experimentation served malicious JavaScript to visitors on Nov. 16 after an attacker added it to their projects inside Optimizely. The code swapped crypto wallet addresses, looked for payment cards typed into. This connects with Robots.txt when the same signal needs a clearer operating decision. A useful companion note is Two Ways Brands Appear in AI Search, because it looks at a nearby part of the same system.
What the visibility signal actually changes: the practical question is whether the page, brand evidence, and surrounding content make the answer easier to trust. If that support is weak, search systems can still understand the topic but fail to connect it confidently to the brand. The same pattern also shows up in WordPress Plugin Update Is the Security Risk, where the practical question is how the signal becomes visible.
What the visibility signal actually changes: that is why the response should begin with an audit of the evidence already on the site before creating a new asset. The fastest improvement is often a clearer page, a better internal link, or a stronger explanation of why the brand belongs in the answer.
Where the evidence needs to be tested
Where the evidence needs to be tested: a single study or ranking observation should not become a strategy by itself. It should become a diagnostic prompt: which source is being trusted, which query pattern is affected, and which part of the site would make that trust easier to earn?
Where the evidence needs to be tested: that keeps the response grounded. The goal is to improve the evidence chain around the topic rather than publish another summary that repeats what every other page already says.
Where the evidence needs to be tested: the important distinction is between a useful signal and a fashionable talking point. A useful signal changes the brief, the page structure, the linking plan, or the measurement view.
How to avoid overreacting to one data point
How to avoid overreacting to one data point: for content teams, the strongest move is to map the claim to existing assets before creating anything new. The right page may already exist, but it may need clearer headings, stronger internal links, fresher proof, or a better explanation of why the brand belongs in the answer.
How to avoid overreacting to one data point: this is also where title rewriting matters. A title should not copy the source headline; it should frame the practical implication so readers immediately know why the topic deserves attention.
How to avoid overreacting to one data point: the same standard should apply to every section. Each heading needs to earn its place by moving the reader through the evidence, not by repeating the outline in a more polished voice.
What this means for content and authority
What this means for content and authority: authority is becoming more contextual. It is not enough to be generally known in a category if the specific answer depends on a different source, a different index, or a different retrieval pattern.
What this means for content and authority: that means the content system should show consistent entities, related pages, credible references, and useful depth around the exact questions people and AI tools are asking.
What this means for content and authority: when the context is weak, AI systems can still mention the brand but describe it in the wrong frame. The fix is not more volume; it is cleaner evidence around the specific association.
Comments
Comments are reviewed before they are published. Links are not allowed inside comments.